Meta Event Match Quality is a score out of 10 that Meta shows in Events Manager for each web event sent through the Conversions API. Meta’s best practices page (checked 2026-10-17) describes it as how effective a server event’s customer information may be at matching it to a Meta account. It is calculated per event, not as one grade for the account. It doesn’t tell you whether a Purchase was real, whether browser and server copies were deduplicated, or whether a campaign will perform better.
That per-event design prevents a lot of wasted work. A PageView happens before most visitors identify themselves. A Login may carry an email and a stable account ID. A Purchase can carry checkout details, browser identifiers and, when the visit came from a Meta ad, a click reference. Different collection moments give different natural ceilings. The useful question is not “How do I make every event reach 10?” but “Does this event send every accurate, permitted identifier that exists at this point in the funnel?”
I use EMQ as one line in a tracking audit, beside delivery, deduplication, consent and reconciliation with the source of truth. The Facebook Conversions API guide explains the payload and hashing rules. This page stays on the score.
Where to find the score
Open Events Manager, select the dataset, and look at the events list. Each web event with server data shows a score out of 10 in the match quality column. Click into the event for the matching details behind it.
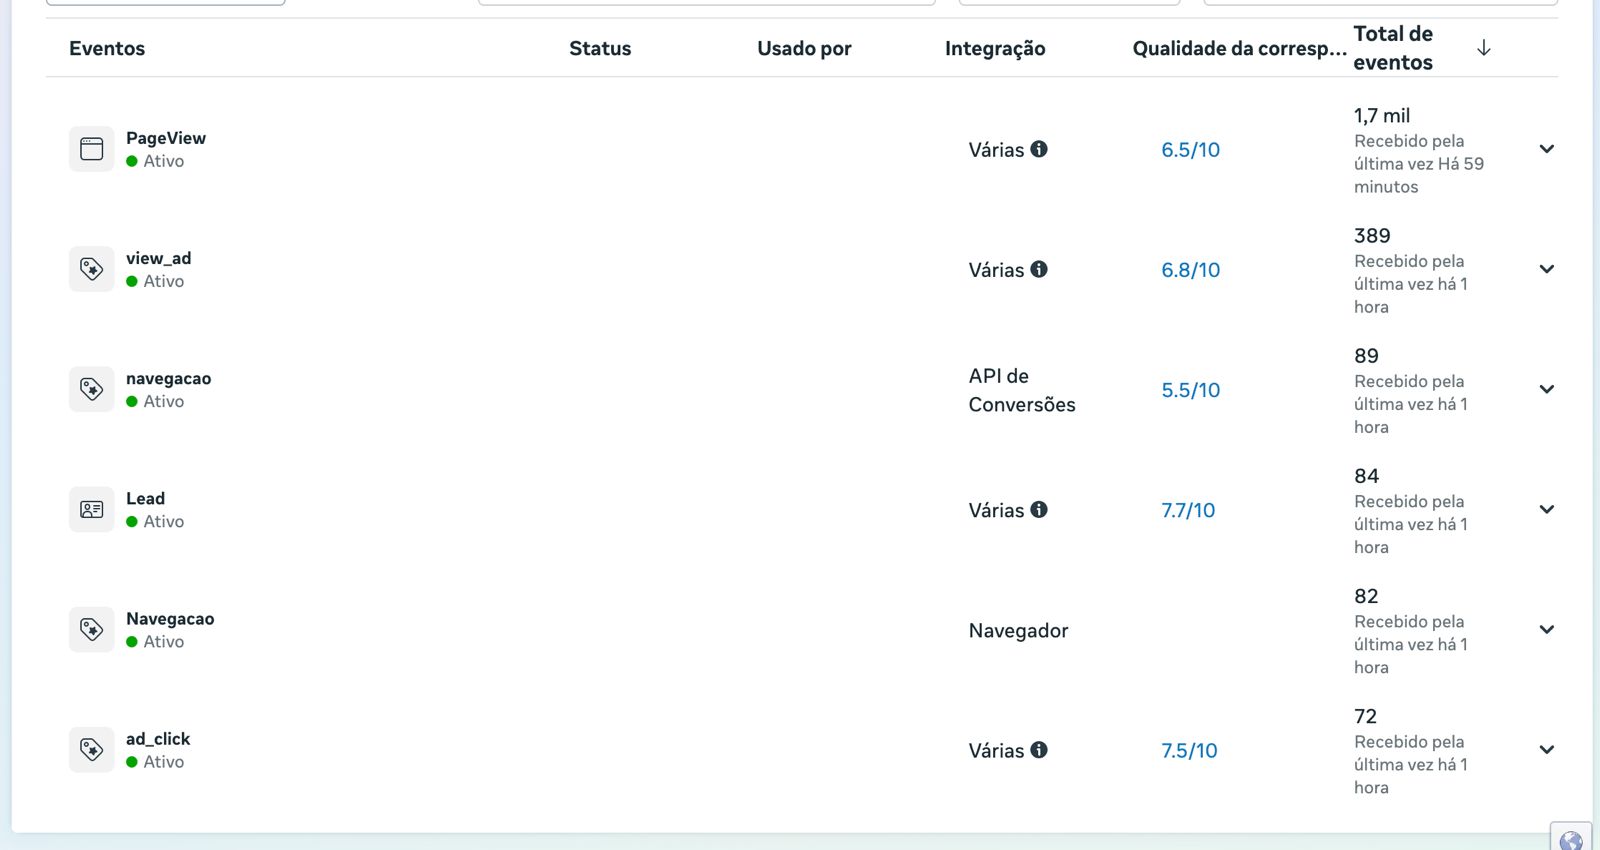
Three things in that capture are worth reading. The scores differ by event, from 5.5 to 7.7, in the same dataset at the same moment. Volume differs too: PageView had about 1,700 events, Lead 84. And the browser-only row, Navegacao, has no score, because EMQ rates the customer information on server events. The list also shows navegacao (Conversions API only) and Navegacao (browser only) as two separate events. If those were meant to be one action, the capitalization difference alone keeps them apart.
What the score measures
Meta does not publish the formula or weighting, so a reverse-engineered equation would be fiction. The safe reading is narrower. Events Manager looks at the identifiers attached to an event’s server traffic, whether those values are usable, and how consistently they arrive. Meta’s best practices name email, IP address, name and phone as high-quality examples. external_id, fbp, fbc and user agent can contribute when they are accurate and appropriate for the event.
The customer information parameter reference defines how each value must be sent. Personal fields are normalized and SHA-256 hashed; browser and click identifiers are not. A higher score means Meta has stronger material for matching. It is still a diagnostic.
| EMQ can help you inspect | EMQ cannot prove |
|---|---|
| Expected identifiers are present on an event | The event represents a real sale or qualified lead |
| A field reaches enough of that event's requests | Browser and server events were deduplicated |
| Formatting and hashing are useful for matching | Attribution is complete |
| A documented payload fix changed the same event | CPA or revenue will improve |
Coverage follows the customer journey
At PageView, the person may be anonymous. The request can carry client IP, user agent and often fbp, but it cannot honestly include an email the visitor hasn’t typed. At Login, the site knows the account, so email and external_id may become available. At Purchase, checkout often supplies email, phone, name, address and an order-linked customer ID, plus fbp and, after a Meta ad click, fbc.
Here coverage means the share of an event’s server requests that carry a hashed email or an external_id. As an illustration, not a measurement: a funnel can show close to 0% on PageView, around half on Login and nearly all on Purchase without anything being broken. Your funnel may collect email at account creation, postpone phone until fulfillment, or let guests buy without logging in. Judge each event against its own data contract:
| Event | What may legitimately exist | What usually does not exist yet |
|---|---|---|
PageView | fbp, client IP, user agent, fbc after a Meta ad click | Email, phone, stable customer ID for an anonymous visitor |
Login | Email, external_id, browser context | Checkout-only phone or address fields |
Purchase | Checkout identifiers, external_id, browser context, a click reference when one was captured | Any field the customer never supplied |
The ceiling is set at collection. A server container can normalize, hash and route a field more reliably, but it cannot create an identifier that never existed. The Meta CAPI with GTM guide covers that routing layer.
fbc belongs where a real click ID was captured
Meta’s fbp and fbc reference (checked 2026-10-17) describes the click ID as the value passed in the URL “when a user clicks an ad on Facebook and/or Instagram”, stored by the Pixel in the _fbc cookie. An fbc value is legitimate when a real fbclid was captured from the landing URL or a valid _fbc cookie exists. A returning visitor may still carry one from an earlier click.
Meta recommends sending fbc with every event. Read that as every event where a real value exists. A journey that never captured an fbclid has nothing to send, and a fabricated value is worse than none. That is why a low fbc coverage figure across all Purchases can make a healthy setup look broken. Measure coverage among sessions that actually arrived with fbclid, not among sessions your analytics tool labels as paid, then check whether those values survived to the server event.
Hosted checkouts often break the chain. The landing page sees the click, but the payment webhook arrives later with no URL or cookie context. The first-party click ID index shows how to store the browser record before the redirect and retrieve it after payment.
Scores move without a setup change
A stable implementation doesn’t receive an identical population every day. The mix shifts among paid and organic traffic, anonymous and logged-in visitors, guest and account checkouts, returning customers, consent states and devices. Each group brings different identifiers. On a low-volume event, a small batch of guest purchases can move the score more than it would on a high-volume event. Meta recalculates the score from received events but doesn’t publish the window or weighting, so a decimal change is not a release monitor.
An oscillation between, say, 8.0 and 9.3 can be normal when nothing changed in the container. Check parameter coverage and the event mix before opening a bug. If email, external_id, fbp and fbc coverage among click-ID sessions stay in their expected ranges, and Purchase still reconciles with the payment system, the movement is not evidence of a broken deployment. Record releases separately.
When the “add email to PageView” warning is noise
The recommendation is noise when it asks a top-funnel event for information that doesn’t exist yet. An anonymous PageView cannot send an accurate email before the visitor types one, creates an account or checks out. The prompt sees a missing parameter. It doesn’t see your form stage, the visitor’s consent choice or the conversion-rate cost of another field.
There are two bad ways to silence it. One is scraping a value from an autofilled form before submission. The other is adding phone or address fields only to raise the score. Send identifiers at the first legitimate event where they exist, such as Login, Lead or Purchase, and leave the earlier event honest.
The same test applies to location fields. The geolocation and EMQ analysis separates a city inferred from the event’s own IP from a customer address collected at checkout.
Fixing a genuinely low score
Fix expected data that gets lost between collection and delivery. The server event reference is the contract for event fields; the customer information reference is the contract for matching fields. A green HTTP response only proves the payload was accepted, not that the values came from the right person or request.
- Pick one event and one recent deployment version.
- Write down the identifiers that should exist at that stage and consent state.
- Run a controlled interaction through the real traffic path. If you automate it, use an ordinary Chrome user agent: in a lab reproduction on 2026-10-06, with a real dataset’s signals configuration, Meta’s Pixel sent nothing from a
HeadlessChromeuser agent. - Inspect the value at collection, in the web request, inside the server container and in the outgoing CAPI payload.
- Correct empty mappings, unstable
external_idvalues, normalization errors, wrong hashing, and IP or user-agent values overwritten by a proxy. - For
fbc, test a real ad-click path and verify the value survives to the conversion. - Publish one identifiable change, wait for enough new events, and compare the same event again.
A managed first-party host such as Stape can keep the server container available, but it doesn’t fill empty parameters. ATA is a Stape affiliate and may earn a commission from that link; the code MRPV20 gives 20% off the first three months.
A high score can still belong to a bad conversion
Meta may match a duplicated Purchase perfectly, or a thank-you page load from a failed payment, or an internal test order with excellent customer data. Test delivery, deduplication and truth separately. Browser and server copies need the same event name and event ID when they describe one action. Purchase counts need to reconcile with approved transactions. Consent has to reach both paths. The server and browser event receipts show how to turn those counts into a recovery audit.
ATA’s next GTM containers, in development, are planned around that order of checks. For Meta today, ATA Edge sends webhook-validated purchases from your own Cloudflare account.
When a changing score comes with different dashboard totals, separate attribution from event delivery before changing the sender.